EstontincPublished 2 min read
Next.js security release, September 2026: which versions to patch and when
Two security updates in one month: a critical remote code execution fix on 22 September and a scheduled release for nine vulnerabilities. What to do now.
If your website or web app runs on Next.js, September 2026 brings two Next.js security updates. On 22 September, the Next.js team shipped an out-of-band fix for a critical remote code execution issue. On 23 September, they announced a scheduled release to fix nine more vulnerabilities, now expected in versions 16.3.8 and 15.5.27.
Here is what each update covers, which versions are affected, and a safe way to patch, based on the official Next.js blog.
Timeline of the September 2026 updates
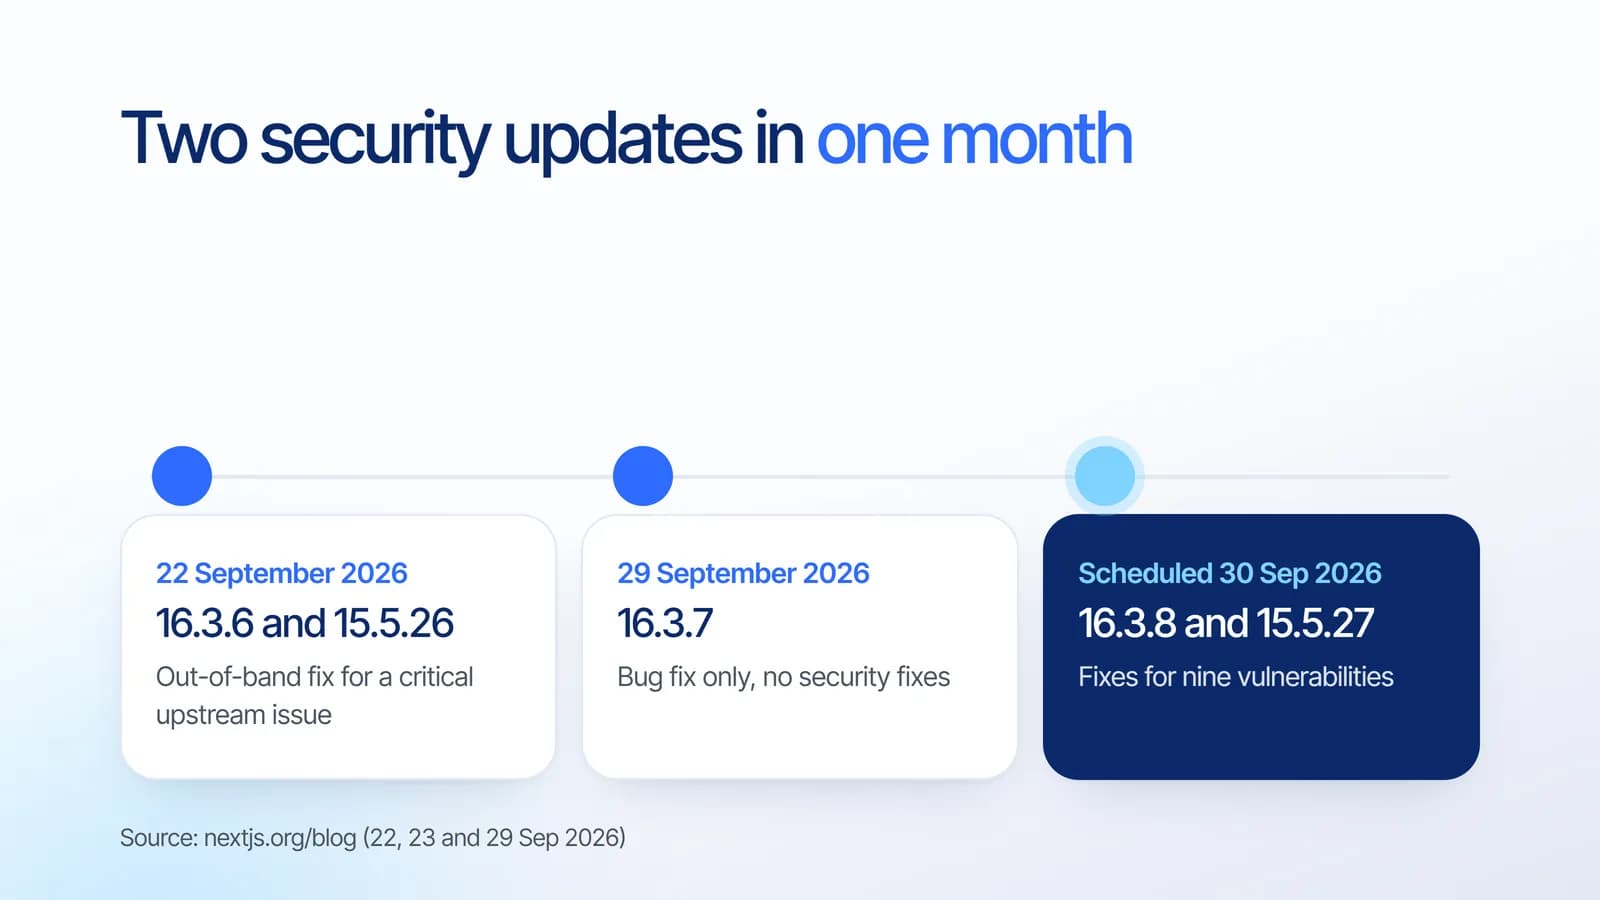
- 22 September 2026: out-of-band security update in 16.3.6 (Active LTS) and 15.5.26 (Maintenance LTS).
- 23 September 2026: announcement of a scheduled security release for 30 September 2026, fixing nine vulnerabilities.
- 29 September 2026: 16.3.7 was published with a bug fix. The Next.js team notes that it does not include the planned security fixes, which are now expected in 16.3.8 and 15.5.27.
At the time of writing (30 September 2026), versions 16.3.8 and 15.5.27 had not yet appeared on npm. We will update this article when they are published.
The 22 September fix: critical remote code execution
The out-of-band release upgrades upstream dependencies, including Satori, to fix an issue that could lead to remote code execution in the Node.js ImageResponse implementation in next/og. Next.js rates it critical (advisory GHSA-vcvr-r3jv-pc5j, with the related upstream advisory GHSA-wx4j-mvgx-mqwp for Satori).
- Affected: Next.js versions from 16.2.0 up to, but not including, 16.3.6.
- Not affected by the remote code execution issue: Next.js 15.x. Version 15.5.26 includes related hardening.
- Not affected: applications that use the Edge ImageResponse implementation.
The scheduled release: nine vulnerabilities
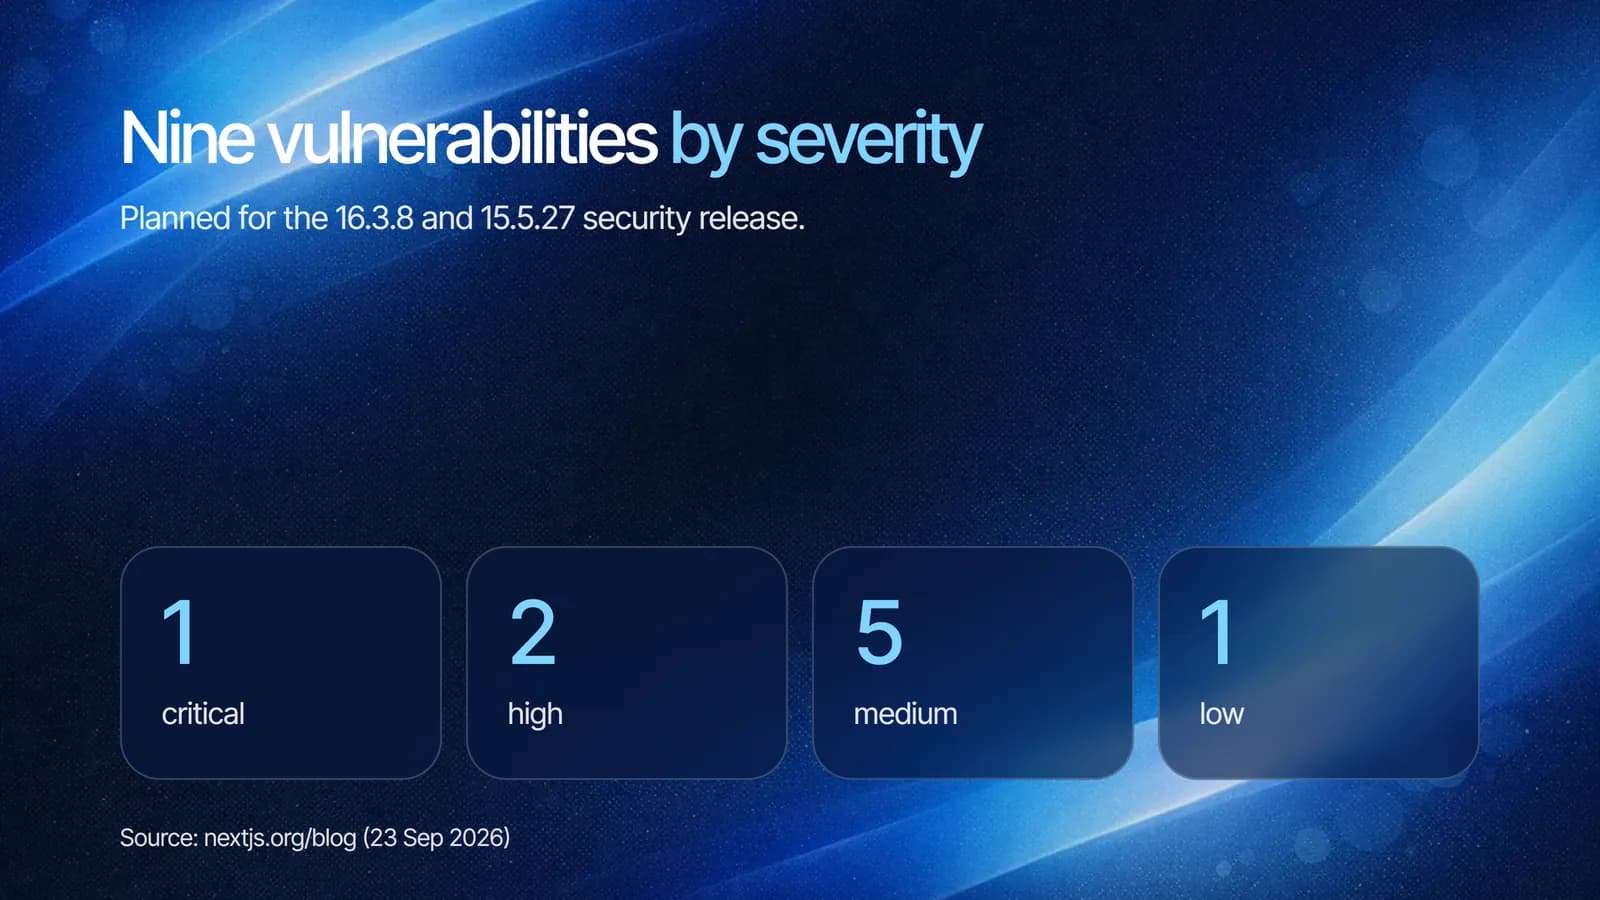
The scheduled release addresses nine vulnerabilities in Next.js: one critical, two high, five medium and one low. The Next.js team plans to publish the full advisories, including impact, affected versions and upgrade instructions, together with the patched versions.
How to patch safely
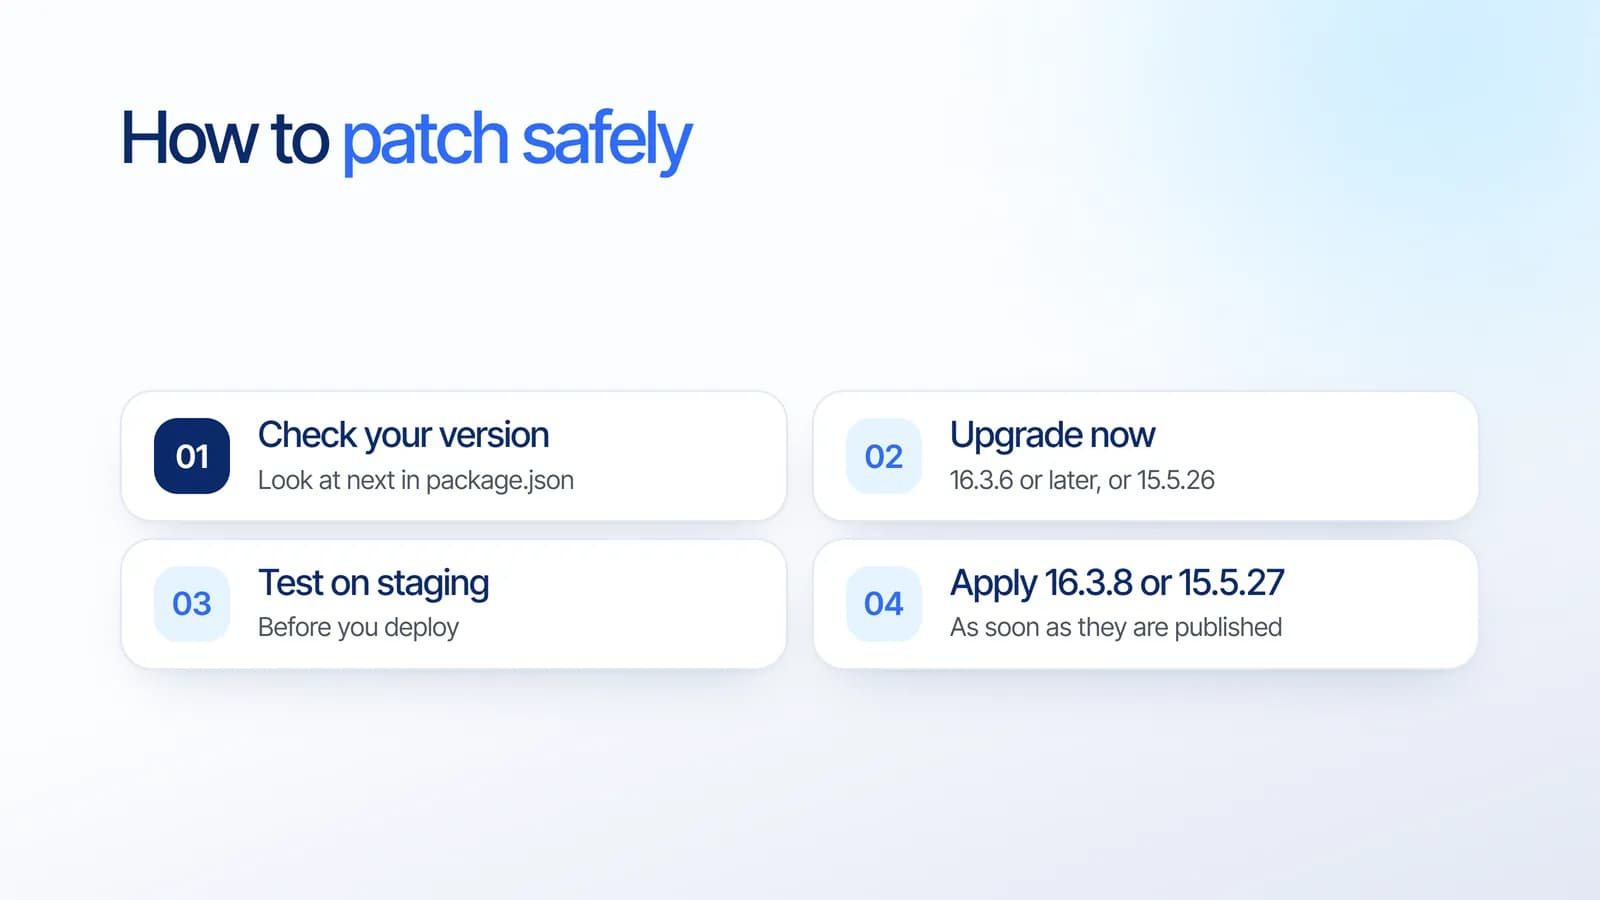
- Check your version. Look at the next package in package.json and in your lockfile.
- Upgrade now. On 16.x, move to 16.3.6 or later. On 15.5, move to 15.5.26. The Next.js blog lists the commands: npm install next@16.3.6 for 16.3, and npm install next@15.5.26 for 15.5.
- Test on staging. Run your main flows, especially pages that generate images with next/og, before deploying.
- Apply 16.3.8 or 15.5.27 as soon as they are published, and read the advisories to see whether any of the nine issues affect features you use.
What it means for your business
Security releases like this are normal for popular frameworks, and a clear upgrade path is a good sign. The real risk is an app that nobody is watching: no one notices the announcement, and the fix sits unapplied for months. A critical remote code execution issue is exactly the kind of problem you want patched within days, not quarters.
This is why we treat maintenance as part of every product, not an optional extra. Our guide to app development cost explains how to budget for it.
How Estontinc can help
We build and maintain Next.js websites and web applications. We can check which version you run, upgrade and test it, and keep it patched through our maintenance plans, which include bug fixes and updates, monitoring and backups. See our web development and cloud & DevOps services.
Not sure which Next.js version your site uses? Ask us to check. We reply within 24 hours.
Frequently asked questions
Which Next.js versions are affected by the 22 September 2026 security issue?
The critical remote code execution issue affects Next.js versions from 16.2.0 up to, but not including, 16.3.6, in the Node.js ImageResponse implementation of next/og. Next.js 15.x is not affected by that issue, and apps using the Edge ImageResponse implementation are not affected.
Which Next.js version should I upgrade to?
Upgrade to 16.3.6 or later on the 16.x line, or 15.5.26 on the 15.5 line, now. Then apply 16.3.8 or 15.5.27 as soon as they are published, because those versions are expected to fix nine more vulnerabilities.
Does Next.js 16.3.7 include the security fixes?
No. The Next.js team says 16.3.7 was published on 29 September 2026 with a bug fix and does not include the security fixes planned for the scheduled release. Those fixes are expected in 16.3.8 and 15.5.27.
How serious are the nine vulnerabilities in the scheduled release?
According to the Next.js blog, the scheduled release addresses nine vulnerabilities: one critical, two high, five medium and one low. Full advisories with impact and affected versions are published together with the patched releases.
Sources
Facts and figures in this article come from these official sources.
- Next.js
- Web development
- App security
- Maintenance